 Cyber Drill
A security check from the attacker's side, for the AI era
Before you are attacked,
know your weak points.
A 30-minute online conversation. We will not ask you to sign anything on the spot.
We put the results in a written report, and state clearly what we did not check.
Old sites that were forgotten, admin pages reachable from outside, and VPN devices that are out of date.
We send realistic training emails and count how many people opened them and how many reported them.
The impact on your business and the order of fixes, in a form you can use yourselves or with another vendor.
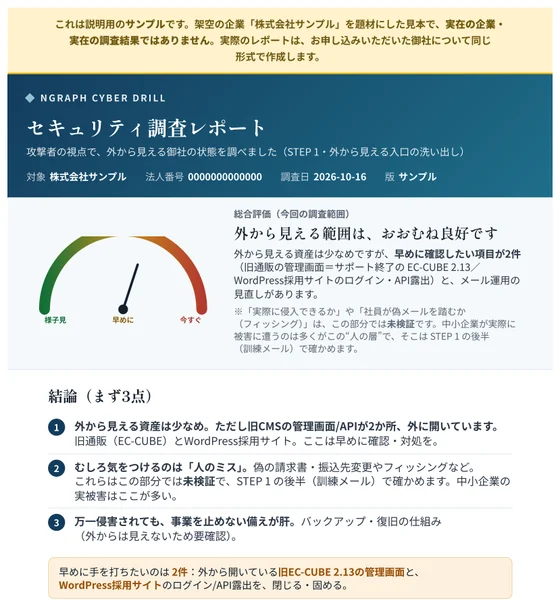 See the sample report (PDF, 5 pages, in Japanese)A sample based on a fictional company
These are National Police Agency figures for the first half of 2026 (January–June) — facts, not fear.
Source: National Police Agency, "Threats in Cyberspace in the First Half of 2026" (published September 2026). Growth rate calculated from the figures in that report
This could be you. That is why we first check the entry points visible from outside.
Attackers use AI. So do we: with AI and testing tools, we map your entry points and test them.
We don't just hand over a report. Watching how you work, we fix settings, permissions and procedures with you.

Protect yourself with settings, permissions, backups and paper procedures, and use products only where those fall short.
We don't stop there — if needed, we fix it and test again. You can also stop after STEP 1.
Regular checkups and ongoing improvement support afterward are also available on request.
What needs fixing depends on what 01 and 02 turn up, so we quote it when we deliver the report.
Attackers use AI too. Let's look together at what could stop your business and how ready you are today.
An expensive product is not always the answer. In STEP 2, we look at how you work and choose a combination of measures like these.
 Keep less, limit access
After checking legal retention duties and business needs, clear out data you don't need to keep. Limit who can view and operate things to only those who need to.
 Keep offline backups
Backups kept off the network, and a check, using data we agree on, that you can actually restore from them.
 Work on paper if needed
Keep emergency contacts and fallback procedures for orders and shipping on paper too, and decide where the paper is kept and how it is updated.
 Prepare your people
Based on the training email results, share with staff how to spot suspicious emails and how to report them.
Only the products you need, only where neededWe start by improving operations and reviewing the settings of your existing systems. Any additional products are chosen by comparing effect, cost and operating burden (our own products are judged by the same standard).
Not included: the cost of equipment or products, large-scale system overhauls, 24-hour monitoring, and emergency recovery after an incident.
Listens to your team and decides what to fix first.
Builds the AI and the testing tools.
Yes. We deliver the report and improvement plan in a form you can use whether you fix things yourselves or hire another company.
We follow procedures that keep the impact low, but we cannot guarantee zero impact. Before we start, we agree in writing on when to stop and how to roll back.
STEP 1 takes about two weeks from the day we agree the scope in writing to the day you receive the report. This includes the period for the training emails to staff. The length of STEP 2 depends on what needs fixing, so we tell you when we deliver the report.
For STEP 1 (reconnaissance, simulated attack, report), we ask about the scope, such as how many sites you have, and give you the price during the free consultation. For STEP 2 (on-site fixes, retest), we quote when we deliver the report, based on the STEP 1 results.
During the pilot period, we are limiting this to companies in Fukui Prefecture.
Immediate incident response itself (containing the breach and restoring systems) is outside our scope. To stop the damage from spreading, please contact the police cyber desk or the IPA (Information-technology Promotion Agency, Japan) first. After things settle, we can help investigate the cause and run a prevention-focused assessment, so feel free to reach out to us as well.
Yes. If you want to use AI without sending company information to outside AI services, see the Local AI Pack. If you want to build AI into your work, see AI Adoption Support (FDE).
In a 30-minute online session, we hear about what could stop your business and how ready you are today. We will not ask you to sign anything on the spot. We usually reply within 2 to 3 business days.